
這是歷史版本頁面 — 看 Zenmap 最新版本
不會用Nmap指令?Zenmap把網路掃描變圖形介面
 Zenmap 6.40
資料更新 2013-07-30
閱讀約 5 分鐘
你剛接手公司網管,或只是想搞清楚家裡網路到底連了哪些裝置。你知道要掃描網路、檢查哪些電腦開了哪些連接埠,但打開命令提示字元輸入指令時,參數一堆根本記不住,輸出結果密密麻麻看不懂。你需要的是一個能幫你把這些事變簡單的工具,而不是再去背指令手冊。
一般人的做法是上網找指令教學,複製貼上然後祈禱結果正確。但Nmap指令參數組合太多,不同掃描類型要配不同參數,貼錯一個字母結果就完全不一樣。這類工具的切入點是:把複雜的指令包裝成圖形介面,用表單和按鈕取代打字,讓你能專注在「想掃什麼」而不是「指令怎麼寫」。
01Zenmap是什麼,跟Nmap有什麼關係?
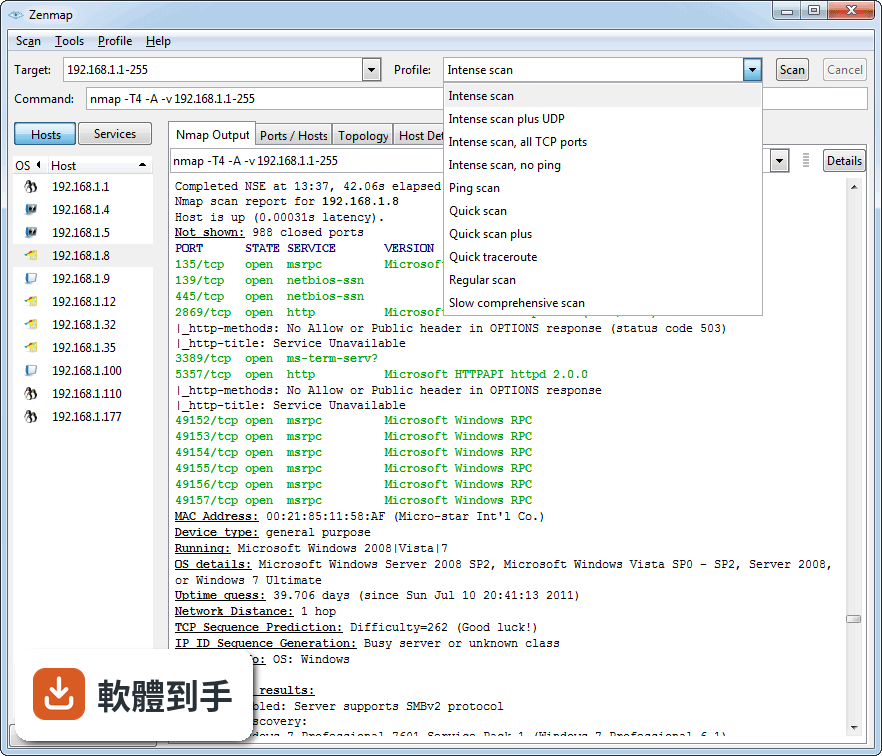
Zenmap是Nmap的官方圖形介面。Nmap本身是命令列工具,功能很強但必須用鍵盤輸入指令。Zenmap把這些指令包裝成視窗介面,你可以在欄位裡輸入目標IP或網域名稱,選好掃描類型,按一下按鈕就開始掃描。安裝Zenmap時會一起裝好Nmap,不需要分開處理。
02這套軟體能掃描哪些目標,只能掃一台電腦嗎?
可以掃描多個目標。除了單一IP位址,也支援輸入IP範圍或子網路,例如192.168.1.0/24這種寫法。也可以直接輸入主機名稱。掃描結果會列出所有找到的裝置、開啟的連接埠和服務,方便你一次掌握整個網路的狀況。
03掃描結果除了看連接埠,還能看到什麼資訊?
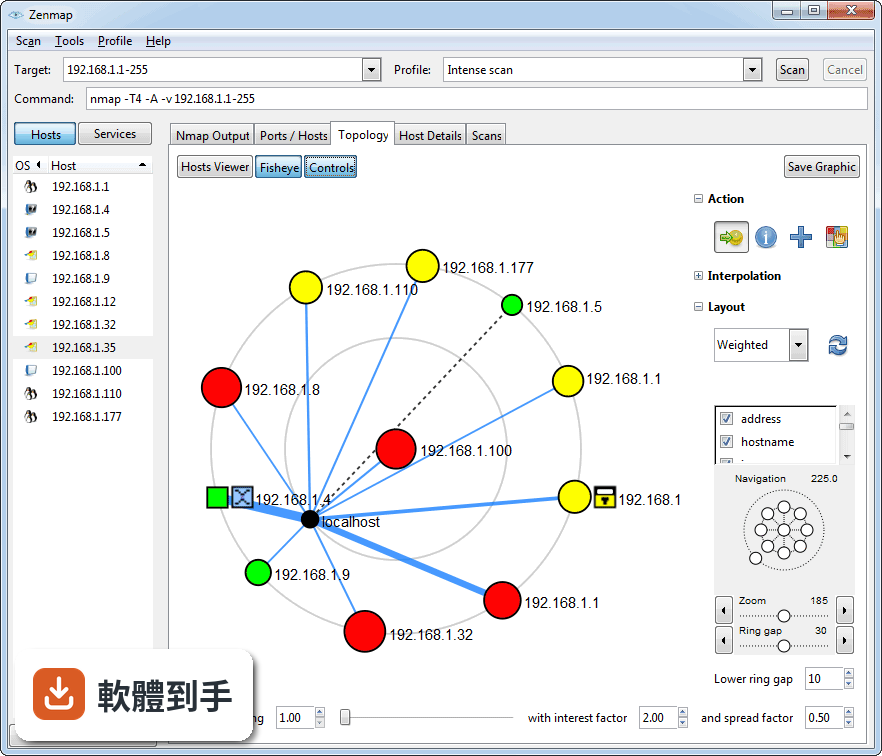
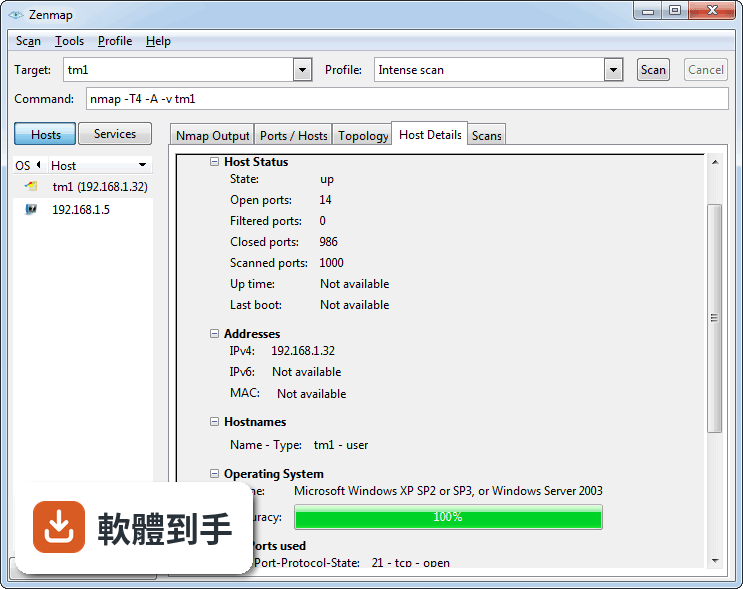
結果分幾個分頁顯示。除了連接埠和服務,還能看到主機詳細資料,包含作業系統偵測結果。另外有拓撲圖分頁,用圖形方式畫出網路裝置之間的連線關係。掃描紀錄會自動保存,之後可以回頭比對不同時間的掃描結果,看網路有沒有出現新的裝置或開啟新的連接埠。
04掃描結果可以存下來嗎?
可以。結果能匯出成XML或純文字格式,方便之後分析或記錄。如果你需要把掃描結果交給別人看,或自己留底比對,這個功能很實用。匯出後可以用其他工具開啟,或直接文字編輯器檢視。
05執行掃描需要管理員權限嗎?
要看掃描類型。基本的掃描可能不需要,但某些掃描像是作業系統偵測或SYN掃描,官方建議要有管理員權限才能完整執行。安裝時也需要管理員權限。如果你在一般使用者帳號下執行,可能會遇到部分功能無法使用的情況。
06我完全不懂網路指令,用這套軟體會卡關嗎?
它的設計就是讓不熟悉命令列的人也能用Nmap。介面有預設的掃描設定檔,例如「Intense scan」和「Quick scan」,直接選就能開始掃描。輸入目標位址、選好設定、按掃描,流程很直覺。不過掃描結果的解讀還是需要一些網路基礎知識,例如知道連接埠號碼代表的服務。
07這套軟體適合哪些人使用?
適合需要做網路安全稽核或管理的IT人員、滲透測試人員和系統管理員。如果你工作上需要定期檢查網路裝置、管理服務升級時程、監控主機或服務是否正常運作,這套軟體能幫你把Nmap的功能用圖形介面操作。對於想學習Nmap的人來說,也可以先從圖形介面理解掃描概念,再慢慢接觸指令。
08這套軟體還在持續更新嗎?
開發更新不算頻繁,屬於偶爾更新的狀態,但官方說明指出它仍然可以搭配新版本的Nmap正常運作。如果你擔心相容性問題,安裝時會一起安裝Nmap,兩者版本會搭配好。介面外觀比較舊,不是現代化的設計風格,但功能上沒有太大問題。
09介面只有英文,看不懂怎麼辦?
這套軟體的介面語系只有英文,沒有繁體中文。如果你英文閱讀有困難,操作上會比較吃力。不過主要欄位和按鈕的英文不算太複雜,配合線上教學或翻譯工具可以克服。如果完全無法接受英文介面,可以考慮其他有中文介面的掃描工具,但功能上可能沒有這麼完整。
10有沒有更簡單的替代軟體?
有。Angry IP Scanner、Advanced IP Scanner、SoftPerfect Network Scanner都是功能相近的掃描工具,介面更簡單,適合只想快速掃描IP和連接埠的使用者。但這些工具的進階功能不如Zenmap完整,例如拓撲圖、掃描紀錄比對、複雜的Nmap參數設定。如果你的需求只是偶爾掃一下網路,這些輕量工具可能更適合。
11非技術人員用這套軟體會遇到什麼困難?
官方說明提到,這套軟體對非技術使用者來說可能難以負擔。雖然圖形介面降低了指令門檻,但掃描結果的判讀、參數的選擇、權限的處理都需要網路基礎知識。如果你只是想知道家裡有哪些裝置連上Wi-Fi,用路由器管理介面或手機App可能更直接。這套軟體是給需要深入分析網路的人用的。
12這套軟體需要付費嗎?
不需要。它是開放原始碼軟體,可以免費下載使用。安裝程式會同時安裝Nmap和Zenmap,不需要額外購買授權。如果你之後想改用其他工具,也因為它是開放原始碼,社群有相關資源可以參考。
下載與官方連結
nmap-6.40-setup.exe · 25.54 MB · 連結指向軟體原廠
版本紀錄
- 2026-03-27 Zenmap 7.99 35.25 MB
- 2025-08-22 Zenmap 7.98 34.56 MB
- 2025-05-14 Zenmap 7.97 34.09 MB
再看 5 筆
- 2025-05-07 Zenmap 7.96 34.04 MB
- 2024-04-23 Zenmap 7.95 32.4 MB
- 2023-05-21 Zenmap 7.94
- 2022-09-02 Zenmap 7.93
- 2021-08-08 Zenmap 7.92
這一版改了什麼
What's new in this version:
- [Nping] Nping now checks for a matching ICMP ID on echo replies, to avoid receiving crosstalk from other ping programs running at the same time.
- [NSE] Added http-adobe-coldfusion-apsa1301.nse. It exploits an authentication bypass vulnerability in Adobe Coldfusion servers.
- [NSE] The ipOps.isPrivate library now considers the deprecated site-local prefix fec0::/10 to be private.
- [Ncat] Added --lua-exec. This feature is basically an equivalent of ncat --sh-exec "lua " and allows you to run Lua scripts with Ncat, redirecting all stdin and stdout operations to the socket connection.
- [NSE] Oops, there was a vulnerability in one of our 437 NSE scripts. If you ran the (fortunately non-default) http-domino-enum-passwords script with the (fortunately also non-default) domino-enum-passwords.idpath parameter against a malicious server, it could cause an arbitrarily named file to to be written to the client system. stdnse.filename_escape function for extra safety.
- [NSE] Added teamspeak2-version.nse
- Nmap's routing table is now sorted first by netmask, then by metric. Previously it was the other way around, which could cause a very general route with a low metric to be preferred over a specific route with a higher metric.
- [Ncat] The -i option (idle timeout) now works in listen mode as well as connect mode.
- Fixed a byte-ordering problem on little-endian architectures when doing idle scan with a zombie that uses broken ID incremements.
- [Ncat] Ncat now support chained certificates with the --ssl-cert option.
- Stop parsing TCP options after reaching EOL in libnetutil.
- [NSE] The dns-ip6-arpa-scan script now optionally accepts "/" syntax for a network mask.
- [Ncat] Reduced the default --max-conns limit from 100 to 60 on Windows, to stay within platform limitations.
- Fixed IPv6 routing table alignment on NetBSD.
- [NSE] Added http-phpmyadmin-dir-traversal
- Added a service probe for Erlang distribution nodes.
- Updated libdnet to not SIOCIFNETMASK before SIOCIFADDR on OpenBSD. This was reported to break on -current as of May 2013.
- Fixed address matching for SCTP (-PY) ping.
- Removed some non-ANSI-C strftime format strings ("%F") and locale-dependent formats ("%c") from NSE scripts and libraries. C99-specified %F
- [Zenmap] Added Polish translation
- [NSE] Added http-coldfusion-subzero. It detects Coldfusion 9 and 10 vulnerable to a local file inclusion vulnerability and grabs the version, install path and the administrator credentials.
- [Nsock] Added a minimal regression test suite for nsock.
- [NSE] Updated redis-brute.nse and redis-info.nse to work against the latest versions of redis server.
- [Ncat] Fixed errors in conneting to IPv6 proxies.
- Added a service probe for Minecraft servers.
- [NSE] Updated hostmap-bfk to work with the latest version of their website.
- [NSE] Added XML structured output support to hostmap-bfk, hostmap-robtex, and hostmap-ip2hosts.
- [NSE] Added hostmap-ip2hosts. It uses the service provider ip2hosts.com to list domain names pointing to the same IP address.
- [NSE] Added http-vuln-cve2013-0156. It detects Ruby on Rails servers vulnerable to remote command execution.
- Added a service probe for the Hazelcast data grid.
- [NSE] Rewrote telnet-brute for better compatibility with a variety of telnet servers.
- [Nsock] Added initial proxy support to nsock. Nsock based modules (version scan, nse) of nmap can now establish TCP connections through chains of proxies. HTTP CONNECT and SOCKS4 protocols are supported, with some limitations.
- Fixed a regression that changed the number of delimiters in machine output.
- [Zenmap] Updated the Italian translation.
- Handle ICMP type 11 (Time Exceeded) responses to port scan probes. Ports will be reported as "filtered", to be consistent with existing Connect scan results, and will have a reason of time-exceeded.
- Add new decoders (BROWSER, DHCP6 and LLMNR) to broadcast-listener and changed output of some of the decoders slightly.
- Timeout script-args are now standardized to use the timespec that Nmap's command-line arguments take (5s, 5000ms, 1h, etc.). Some scripts that previously took an integer number of milliseconds will now treat that as a number of seconds if not explicitly denoted as ms.
- The list of nameservers on Windows now ignores nameservers from inactive interfaces.
- Namespace the pipes used to communicate with subprocesses by PID, to avoid multiple instances of Ncat from interfering with each other.
- Nmap may now partially rearrange its target list for more efficient host groups. Previously, a single target with a different interface, or with an IP address the same as a that of a target already in the group, would cause the group to be broken off at whatever size it was. Now, we buffer a small number of such targets, and keep looking through the input for more targets to fill out the current group.
- [NSE] Changed ip-geolocation-geoplugin to use the web service's new output format.
- Limited the number of open sockets in ultra_scan to FD_SETSIZE. Very fast connect scans could write past the end of an fd_set and cause a variety of crashes: nmap: scan_engine.cc:978: bool ConnectScanInfo::clearSD(int): Assertion `numSDs > 0' failed. select failed in do_one_select_round(): Bad file descriptor (9)
- Fixed a bug that prevented Nmap from finding any interfaces when one of them had the type ARP_HDR_APPLETALK; this was the case for AppleTalk interfaces. However, This support is not complete since AppleTalk interfaces use different size hardware addresses than Ethernet. Nmap IP level scans should work without any problem
- [Nping] Nping now skips localhost targets for privileged pings (with an error message) because those generally don't work.
- [Ncat] Ncat now keeps running in connect mode after receiving EOF from the remote socket, unless --recv-only is in effect.
- Routes are now sorted to prefer those with a lower metric. Retrieval of metrics is supported only on Linux and Windows. [David Fifield]
- Packet trace of ICMP packets now include the ICMP ID and sequence number by default.
- [NSE] Added ike-version and a new ike library
- [NSE] Fixed various NSEDoc bugs
- [Zenmap] Zenmap now understands the NMAP_PRIVILEGED and NMAP_UNPRIVILEGED environment variables.
- It's now possible to mix IPv4 range notation with CIDR netmasks in target specifications. For example, 192.168-170.4-100,200.5/16 is effectively the same as 192.168.168-170.0-255.0-255.
- Added nmap-fo.xsl, This converts Nmap XML into XSL-FO, which can be converted into PDF using Apache FOP.
- Increased the number of slack file descriptors not used during connect scan. Previously, the calculation did not consider the descriptors used by various open log files. Connect scans using a lot of sockets could fail with the message "Socket creation in sendConnectScanProbe: Too many open files".
- [Zenmap] Fixed internationalization files. Running in a language other than the default English would result in the error "ValueError: too many values to unpack".
- Changed the --webxml XSL stylesheet to point to the new location of nmap.xsl in the new respository,
- [NSE] Made the vulnerability library able to preserve vulnerability information across multiple ports of the same host.
- [NSE] Added ventrilo-info, This gets information from a Ventrilo VoIP server.
- Removed the undocumented -q option, which renamed the nmap process to something like "pine".
- Moved the Japanese man page from man1/jp to man1/ja. jp is a country code while ja is a language code.
- [NSE] Added mysql-enum script which enumerates valid mysql server usernames
- [Nsock] Reworked the logging infrastructure to make it more flexible and consistent. Updated nmap, nping and ncat accordingly. Nsock log level can now be adjusted at runtime by pressing d/D in nmap.
- [NSE] Fixed scripts using unconnected UDP sockets.
- [NSE] Added structured output to http-git.nse.
- [NSE] Added murmur-version, This gets the server version and other information for Murmur, the server for the Mumble VoIP system.
- Added a corresponding UDP payload for Murmur.
- [Zenmap] Fixed a crash that could be caused by opening the About dialog, using the window manager to close it, and opening it again.
- [Ncat] Made test-addrset.sh exit with nonzero status if any tests fail. This in turn causes "make check" to fail if any tests fail.
- Fixed compilation with --without-liblua.
- Fixed CRC32c calculation (as used in SCTP scans) on 64-bit platforms.
- [NSE] Added multicast group name output to broadcast-igmp-discovery.nse.
- [NSE] Added new fingerprints for http-enum: Sitecore, Moodle, typo3, SquirrelMail, RoundCube.