
這是歷史版本頁面 — 看 Zenmap 最新版本
不會用Nmap指令?Zenmap把網路掃描變圖形介面
 Zenmap 7.92
資料更新 2021-08-08
閱讀約 5 分鐘
你剛接手公司網管,或只是想搞清楚家裡網路到底連了哪些裝置。你知道要掃描網路、檢查哪些電腦開了哪些連接埠,但打開命令提示字元輸入指令時,參數一堆根本記不住,輸出結果密密麻麻看不懂。你需要的是一個能幫你把這些事變簡單的工具,而不是再去背指令手冊。
一般人的做法是上網找指令教學,複製貼上然後祈禱結果正確。但Nmap指令參數組合太多,不同掃描類型要配不同參數,貼錯一個字母結果就完全不一樣。這類工具的切入點是:把複雜的指令包裝成圖形介面,用表單和按鈕取代打字,讓你能專注在「想掃什麼」而不是「指令怎麼寫」。
01Zenmap是什麼,跟Nmap有什麼關係?
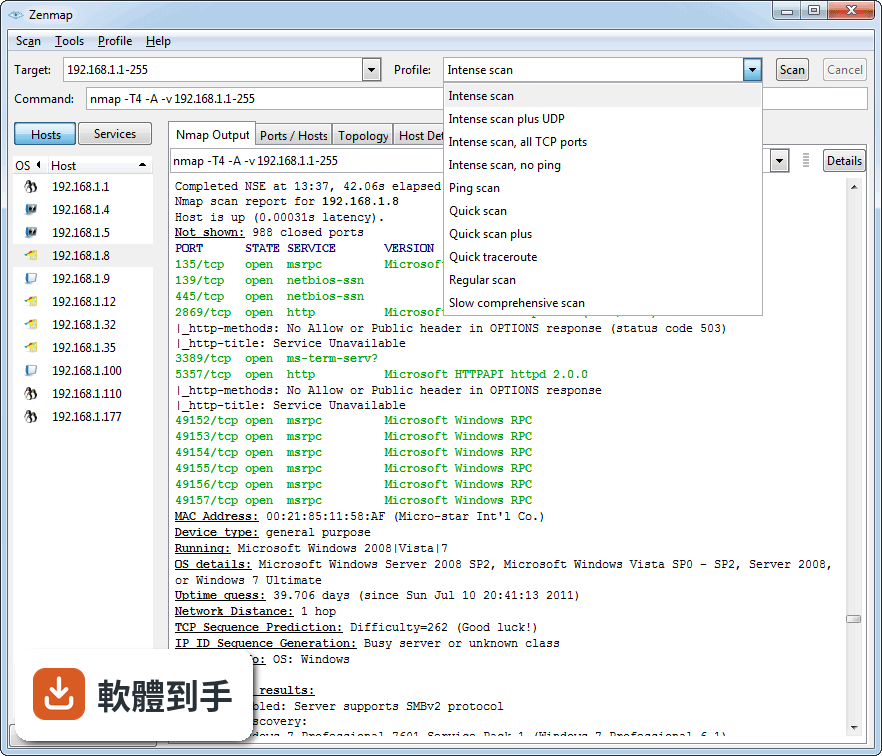
Zenmap是Nmap的官方圖形介面。Nmap本身是命令列工具,功能很強但必須用鍵盤輸入指令。Zenmap把這些指令包裝成視窗介面,你可以在欄位裡輸入目標IP或網域名稱,選好掃描類型,按一下按鈕就開始掃描。安裝Zenmap時會一起裝好Nmap,不需要分開處理。
02這套軟體能掃描哪些目標,只能掃一台電腦嗎?
可以掃描多個目標。除了單一IP位址,也支援輸入IP範圍或子網路,例如192.168.1.0/24這種寫法。也可以直接輸入主機名稱。掃描結果會列出所有找到的裝置、開啟的連接埠和服務,方便你一次掌握整個網路的狀況。
03掃描結果除了看連接埠,還能看到什麼資訊?
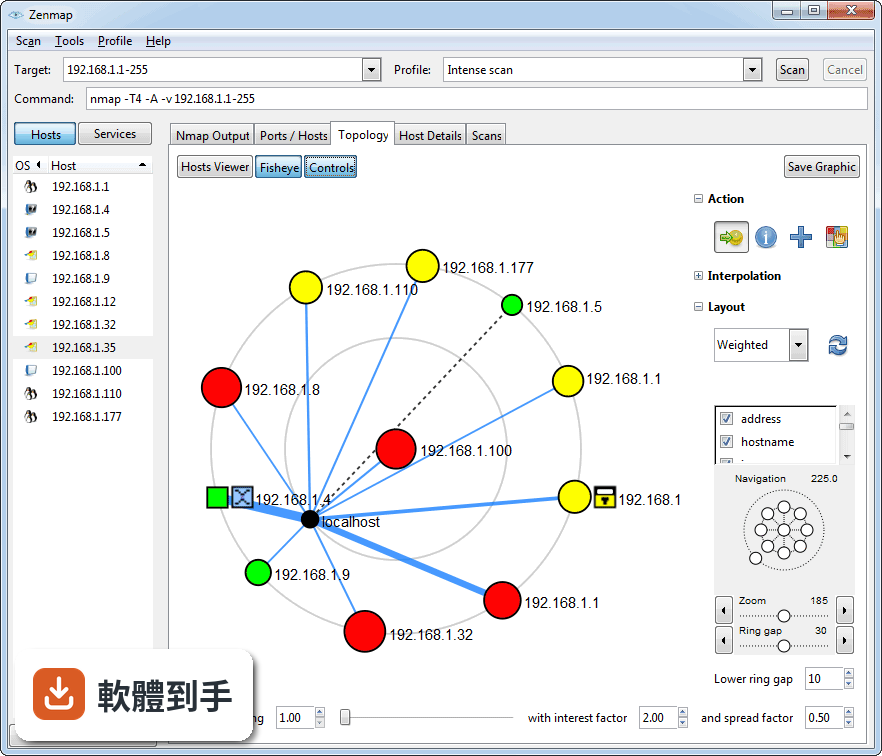
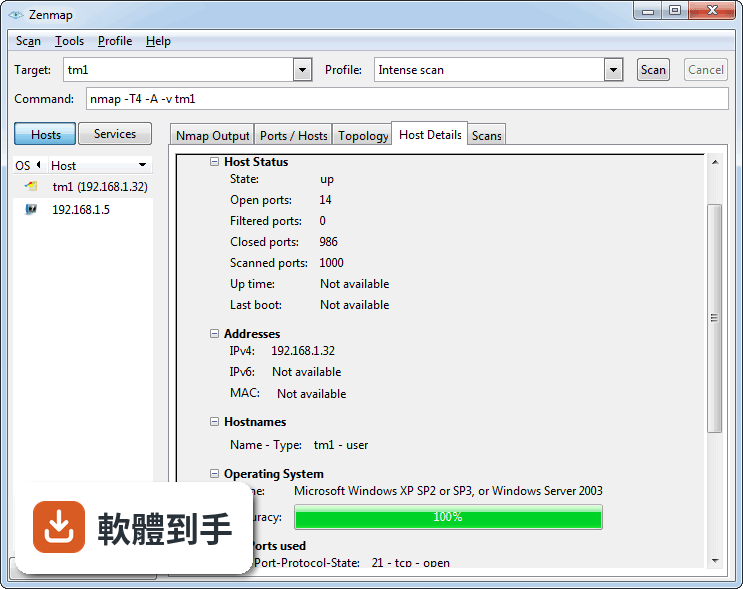
結果分幾個分頁顯示。除了連接埠和服務,還能看到主機詳細資料,包含作業系統偵測結果。另外有拓撲圖分頁,用圖形方式畫出網路裝置之間的連線關係。掃描紀錄會自動保存,之後可以回頭比對不同時間的掃描結果,看網路有沒有出現新的裝置或開啟新的連接埠。
04掃描結果可以存下來嗎?
可以。結果能匯出成XML或純文字格式,方便之後分析或記錄。如果你需要把掃描結果交給別人看,或自己留底比對,這個功能很實用。匯出後可以用其他工具開啟,或直接文字編輯器檢視。
05執行掃描需要管理員權限嗎?
要看掃描類型。基本的掃描可能不需要,但某些掃描像是作業系統偵測或SYN掃描,官方建議要有管理員權限才能完整執行。安裝時也需要管理員權限。如果你在一般使用者帳號下執行,可能會遇到部分功能無法使用的情況。
06我完全不懂網路指令,用這套軟體會卡關嗎?
它的設計就是讓不熟悉命令列的人也能用Nmap。介面有預設的掃描設定檔,例如「Intense scan」和「Quick scan」,直接選就能開始掃描。輸入目標位址、選好設定、按掃描,流程很直覺。不過掃描結果的解讀還是需要一些網路基礎知識,例如知道連接埠號碼代表的服務。
07這套軟體適合哪些人使用?
適合需要做網路安全稽核或管理的IT人員、滲透測試人員和系統管理員。如果你工作上需要定期檢查網路裝置、管理服務升級時程、監控主機或服務是否正常運作,這套軟體能幫你把Nmap的功能用圖形介面操作。對於想學習Nmap的人來說,也可以先從圖形介面理解掃描概念,再慢慢接觸指令。
08這套軟體還在持續更新嗎?
開發更新不算頻繁,屬於偶爾更新的狀態,但官方說明指出它仍然可以搭配新版本的Nmap正常運作。如果你擔心相容性問題,安裝時會一起安裝Nmap,兩者版本會搭配好。介面外觀比較舊,不是現代化的設計風格,但功能上沒有太大問題。
09介面只有英文,看不懂怎麼辦?
這套軟體的介面語系只有英文,沒有繁體中文。如果你英文閱讀有困難,操作上會比較吃力。不過主要欄位和按鈕的英文不算太複雜,配合線上教學或翻譯工具可以克服。如果完全無法接受英文介面,可以考慮其他有中文介面的掃描工具,但功能上可能沒有這麼完整。
10有沒有更簡單的替代軟體?
有。Angry IP Scanner、Advanced IP Scanner、SoftPerfect Network Scanner都是功能相近的掃描工具,介面更簡單,適合只想快速掃描IP和連接埠的使用者。但這些工具的進階功能不如Zenmap完整,例如拓撲圖、掃描紀錄比對、複雜的Nmap參數設定。如果你的需求只是偶爾掃一下網路,這些輕量工具可能更適合。
11非技術人員用這套軟體會遇到什麼困難?
官方說明提到,這套軟體對非技術使用者來說可能難以負擔。雖然圖形介面降低了指令門檻,但掃描結果的判讀、參數的選擇、權限的處理都需要網路基礎知識。如果你只是想知道家裡有哪些裝置連上Wi-Fi,用路由器管理介面或手機App可能更直接。這套軟體是給需要深入分析網路的人用的。
12這套軟體需要付費嗎?
不需要。它是開放原始碼軟體,可以免費下載使用。安裝程式會同時安裝Nmap和Zenmap,不需要額外購買授權。如果你之後想改用其他工具,也因為它是開放原始碼,社群有相關資源可以參考。
下載與官方連結
nmap-7.92-setup.exe · 連結指向軟體原廠
版本紀錄
- 2026-03-27 Zenmap 7.99 35.25 MB
- 2025-08-22 Zenmap 7.98 34.56 MB
- 2025-05-14 Zenmap 7.97 34.09 MB
再看 5 筆
- 2025-05-07 Zenmap 7.96 34.04 MB
- 2024-04-23 Zenmap 7.95 32.4 MB
- 2023-05-21 Zenmap 7.94
- 2022-09-02 Zenmap 7.93
- 2021-08-08 Zenmap 7.92
這一版改了什麼
What's new in this version:
- [Windows] Upgraded Npcap (our Windows raw packet capturing and transmission driver) from version 1.00 to the latest version 1.50.
- [Windows] Thanks to the Npcap 1.50 upgrade, Nmap now works on the Windows ARM architecture so you can run it on lightweight and power-efficient tablets like the Microsoft Surface Pro X and Samsung Galaxy Book Go. More ARM devices are on the way along with the upcoming Windows 11 release.
- [Windows] Updated our Windows builds to Visual Studio 2019, Windows 10 SDK, and the UCRT. This prevents Nmap from working on Windows Vista and earlier, but they can still use older versions of Nmap on their ancient operating system.
- New Nmap option --unique will prevent Nmap from scanning the same IP address twice, which can happen when different names resolve to the same address.
- [NSE][GH#1691] TLS 1.3 now supported by most scripts for which it is relevant, such as ssl-enum-ciphers. Some functions like ssl tunnel connections and certificate parsing will require OpenSSL 1.1.1 or later to fully support TLS 1.3.
[NSE] Added 3 NSE scripts, from 4 authors, bringing the total up to 604!, and the summaries are below:
- [GH#2201] nbns-interfaces queries NetBIOS name service (NBNS) to gather IP addresses of the target's network interfaces
- [GH#711] openflow-info gathers preferred and supported protocol versions from OpenFlow devices
- port-states prints a list of ports that were found in each state, including states that were summarized as "Not shown: X closed ports"
- [GH#2350] Upgraded OpenSSL to version 1.1.1k. This addresses some CVE's which don't affect Nmap in a material way.
- Removed support for the ancient WinPcap library since we already include our own Npcap library supporting the same API. WinPcap was abandoned years ago and it's official download page says that "WE RECOMMEND USING Npcap INSTEAD" for security, stability, compatibility, and support reasons.
- [GH#2257] Fix an issue in addrset matching that was causing all targets to be excluded if the --excludefile listed a CIDR range that contains an earlier, smaller CIDR range.
- Upgrade the Windows NSIS installer to use the latest NSIS 3 (version 3.07) instead of the previous NSIS 2 generation.
- Setting --host-timeout=0 will disable the host timeout, which is set by -T5 to 15 minutes. Earlier versions of Nmap require the user to specify a very long timeout instead.
Several changes to UDP payloads to improve accuracy:
- [GH#2269] Fix an issue with -sU where payload data went out-of-scope before it was used, causing corrupted payloads to be sent.
- Nmap's retransmission limits were preventing some UDP payloads from being tried with -sU and -PU. Now, Nmap sends each payload for a particular port at the same time without delay.
New UDP payloads:
- [GH#1279] TS3INIT1 for UDP 3389
- [GH#1895] DTLS for UDP 3391 (RD Gateway)
[NSE][GH#2208][GH#2203] SMB2 dialect handling has been redesigned. Visible changes include:
- Notable improvement in speed of script smb-protocols and others
- Some SMB scripts are no longer using a hardcoded dialect, improving target interoperability
- Dialect names are aligned with Microsoft, such as 3.0.2, instead of 3.02
Improvements to Nmap's XML output:
- If a host times out, the XML <host> element will have the attribute timedout="true" and the host's timing info (srtt etc.) will still be printed.
- The "extrareasons" element now includes a list of port numbers for each "ignored" state. The "All X ports" and "Not shown:" lines in normal output have been changed slightly to provide more detail.
- [NSE][GH#2237] Prevent the ssl-* NSE scripts from probing ports that were excluded from version scan, usually 9100-9107, since JetDirect will print anything sent to these ports.
- [GH#2206] Nmap no longer produces cryptic message "Failed to convert source address to presentation format" when unable to find useable route to the target.
- [Ncat][GH#2202] Use safety-checked versions of FD_* macros to abort early if number of connections exceeds FD_SETSIZE.
- [Ncat] Connections proxied via SOCKS4/SOCKS5 were intermittently dropping server data sent right after the connection got established, such as port banners.
- [Ncat][GH#2149] Fixed a bug in proxy connect mode which would close the connection as soon as it was opened in Nmap 7.90 and 7.91.
- [NSE][GH#2175] Fixed NSE so it will not consolidate all port script output for targets which share an IP (e.g. HTTP vhosts) under one target.
- [Zenmap][GH#2157] Fixed an issue where a failure to execute Nmap would result in a Zenmap crash with "TypeError: coercing to Unicode" exception.
- Nmap no longer considers an ICMP Host Unreachable as confirmation that a target is down, in accordance with RFC 1122 which says these errors may be transient. Instead, the probe will be destroyed and other probes used to determine aliveness.
- [Ncat][GH#2154] Ncat no longer crashes when used with Unix domain sockets.
- [Ncat][GH#2167][GH#2168] Ncat is now again generating certificates with the duration of one year. Due to a bug, recent versions of Ncat were using only one minute.
- [NSE][GH#2281] URL/percent-encoding is now using uppercase hex digits to align with RFC 3986, section 2.1, and to improve compatibility with some real-world web servers.
- [NSE][GH#2174] Script hostmap-crtsh got improved in several ways. The most visible are that certificate SANs are properly split apart and that identities that are syntactically incorrect to be hostnames are now ignored.
- [NSE] Loading of a Nikto database failed if the file was referenced relative to the Nmap directory
- [GH#2199] Updated Nmap's NPSL license to rewrite a poorly-worded clause abiyt "proprietary software companies". As described on that page, we are also still offering Nmap 7.90, 7.91, and 7.92 under the previous Nmap 7.80 license. Finally, we still offer the Nmap OEM program for companies who want a non-copyleft license allowing them to redistribute Nmap with their products.
- [NSE] Script smb2-vuln-uptime no longer reports false positives when the target does not provide its boot time.
- [NSE][GH#2197] Client packets composed by the DHCP library will now contain option 51 (IP address lease time) only when requested.
- [NSE][GH#2192] XML decoding in library citrixxml no longer crashes when encountering a character reference with codepoint greater than 255. (These references are now left unmodified.)
- [NSE] Script mysql-audit now defaults to the bundled mysql-cis.audit for the audit rule base.
- [NSE][GH#1473] It is now possible to control whether the SNMP library uses v1 (default) or v2c by setting script argument snmp.version.