
這是歷史版本頁面 — 看 Zenmap 最新版本
不會用Nmap指令?Zenmap把網路掃描變圖形介面
 Zenmap 7.50
資料更新 2017-06-15
閱讀約 5 分鐘
你剛接手公司網管,或只是想搞清楚家裡網路到底連了哪些裝置。你知道要掃描網路、檢查哪些電腦開了哪些連接埠,但打開命令提示字元輸入指令時,參數一堆根本記不住,輸出結果密密麻麻看不懂。你需要的是一個能幫你把這些事變簡單的工具,而不是再去背指令手冊。
一般人的做法是上網找指令教學,複製貼上然後祈禱結果正確。但Nmap指令參數組合太多,不同掃描類型要配不同參數,貼錯一個字母結果就完全不一樣。這類工具的切入點是:把複雜的指令包裝成圖形介面,用表單和按鈕取代打字,讓你能專注在「想掃什麼」而不是「指令怎麼寫」。
01Zenmap是什麼,跟Nmap有什麼關係?
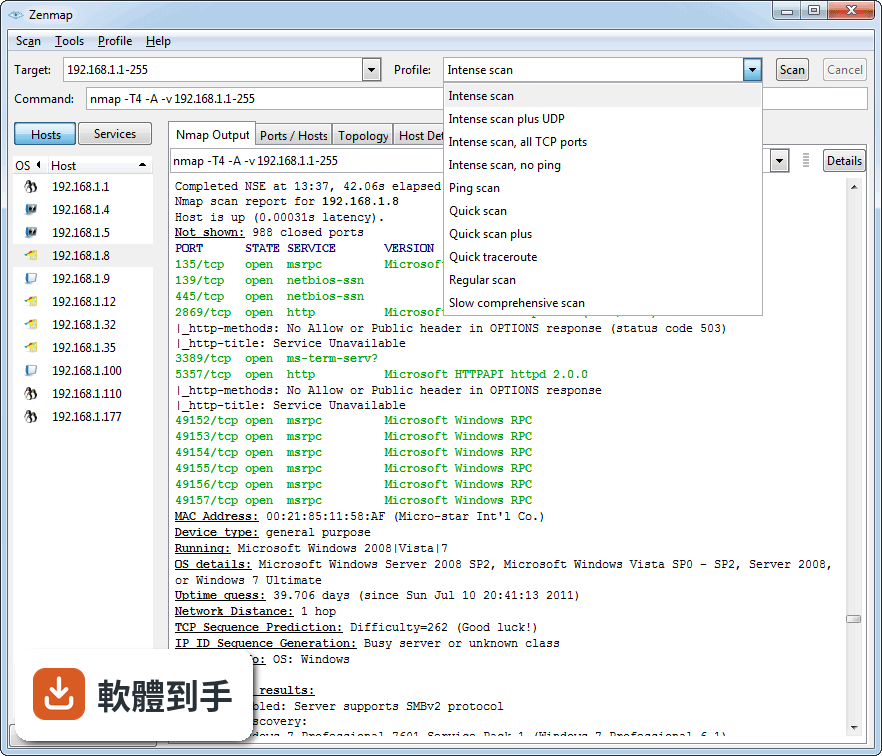
Zenmap是Nmap的官方圖形介面。Nmap本身是命令列工具,功能很強但必須用鍵盤輸入指令。Zenmap把這些指令包裝成視窗介面,你可以在欄位裡輸入目標IP或網域名稱,選好掃描類型,按一下按鈕就開始掃描。安裝Zenmap時會一起裝好Nmap,不需要分開處理。
02這套軟體能掃描哪些目標,只能掃一台電腦嗎?
可以掃描多個目標。除了單一IP位址,也支援輸入IP範圍或子網路,例如192.168.1.0/24這種寫法。也可以直接輸入主機名稱。掃描結果會列出所有找到的裝置、開啟的連接埠和服務,方便你一次掌握整個網路的狀況。
03掃描結果除了看連接埠,還能看到什麼資訊?
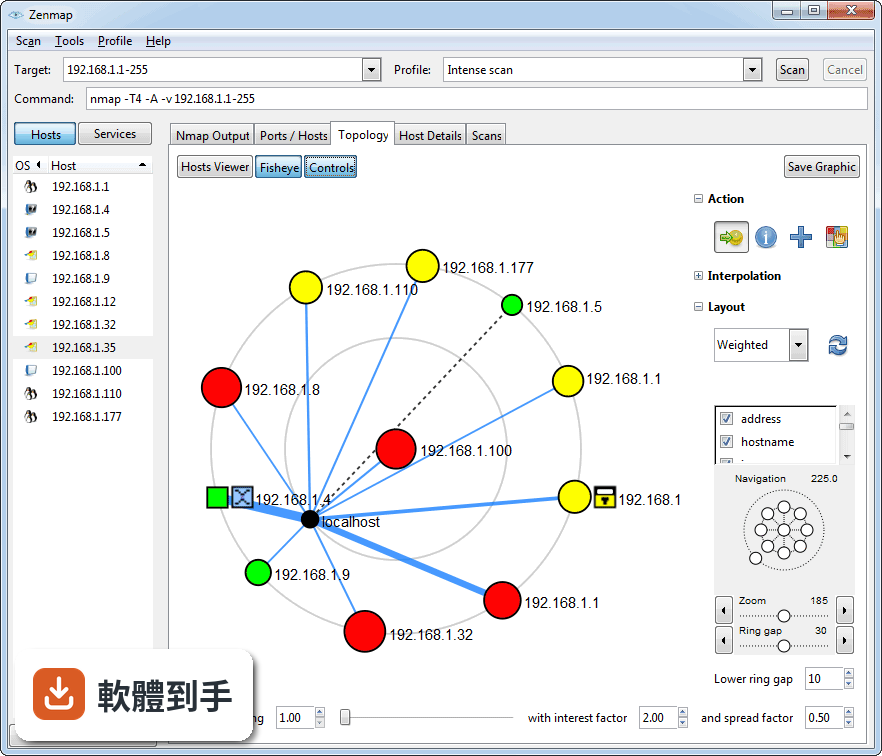
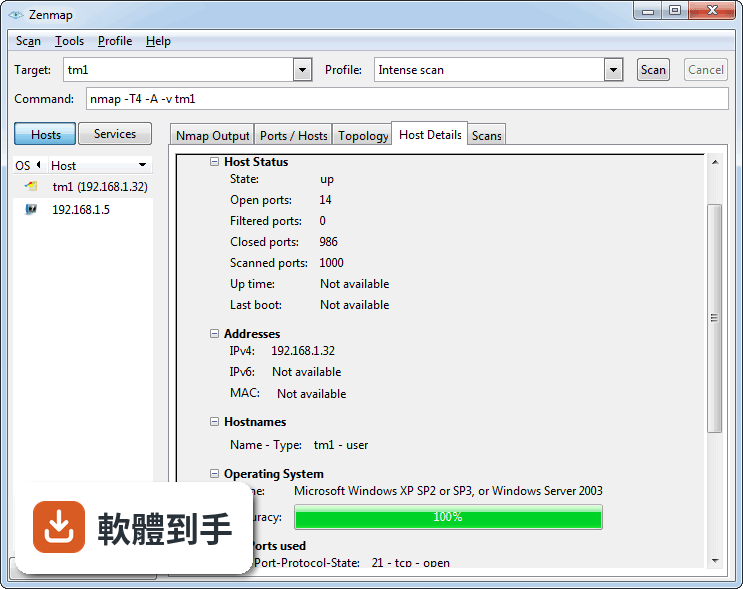
結果分幾個分頁顯示。除了連接埠和服務,還能看到主機詳細資料,包含作業系統偵測結果。另外有拓撲圖分頁,用圖形方式畫出網路裝置之間的連線關係。掃描紀錄會自動保存,之後可以回頭比對不同時間的掃描結果,看網路有沒有出現新的裝置或開啟新的連接埠。
04掃描結果可以存下來嗎?
可以。結果能匯出成XML或純文字格式,方便之後分析或記錄。如果你需要把掃描結果交給別人看,或自己留底比對,這個功能很實用。匯出後可以用其他工具開啟,或直接文字編輯器檢視。
05執行掃描需要管理員權限嗎?
要看掃描類型。基本的掃描可能不需要,但某些掃描像是作業系統偵測或SYN掃描,官方建議要有管理員權限才能完整執行。安裝時也需要管理員權限。如果你在一般使用者帳號下執行,可能會遇到部分功能無法使用的情況。
06我完全不懂網路指令,用這套軟體會卡關嗎?
它的設計就是讓不熟悉命令列的人也能用Nmap。介面有預設的掃描設定檔,例如「Intense scan」和「Quick scan」,直接選就能開始掃描。輸入目標位址、選好設定、按掃描,流程很直覺。不過掃描結果的解讀還是需要一些網路基礎知識,例如知道連接埠號碼代表的服務。
07這套軟體適合哪些人使用?
適合需要做網路安全稽核或管理的IT人員、滲透測試人員和系統管理員。如果你工作上需要定期檢查網路裝置、管理服務升級時程、監控主機或服務是否正常運作,這套軟體能幫你把Nmap的功能用圖形介面操作。對於想學習Nmap的人來說,也可以先從圖形介面理解掃描概念,再慢慢接觸指令。
08這套軟體還在持續更新嗎?
開發更新不算頻繁,屬於偶爾更新的狀態,但官方說明指出它仍然可以搭配新版本的Nmap正常運作。如果你擔心相容性問題,安裝時會一起安裝Nmap,兩者版本會搭配好。介面外觀比較舊,不是現代化的設計風格,但功能上沒有太大問題。
09介面只有英文,看不懂怎麼辦?
這套軟體的介面語系只有英文,沒有繁體中文。如果你英文閱讀有困難,操作上會比較吃力。不過主要欄位和按鈕的英文不算太複雜,配合線上教學或翻譯工具可以克服。如果完全無法接受英文介面,可以考慮其他有中文介面的掃描工具,但功能上可能沒有這麼完整。
10有沒有更簡單的替代軟體?
有。Angry IP Scanner、Advanced IP Scanner、SoftPerfect Network Scanner都是功能相近的掃描工具,介面更簡單,適合只想快速掃描IP和連接埠的使用者。但這些工具的進階功能不如Zenmap完整,例如拓撲圖、掃描紀錄比對、複雜的Nmap參數設定。如果你的需求只是偶爾掃一下網路,這些輕量工具可能更適合。
11非技術人員用這套軟體會遇到什麼困難?
官方說明提到,這套軟體對非技術使用者來說可能難以負擔。雖然圖形介面降低了指令門檻,但掃描結果的判讀、參數的選擇、權限的處理都需要網路基礎知識。如果你只是想知道家裡有哪些裝置連上Wi-Fi,用路由器管理介面或手機App可能更直接。這套軟體是給需要深入分析網路的人用的。
12這套軟體需要付費嗎?
不需要。它是開放原始碼軟體,可以免費下載使用。安裝程式會同時安裝Nmap和Zenmap,不需要額外購買授權。如果你之後想改用其他工具,也因為它是開放原始碼,社群有相關資源可以參考。
下載與官方連結
nmap-7.50-setup.exe · 26.01 MB · 連結指向軟體原廠
版本紀錄
- 2026-03-27 Zenmap 7.99 35.25 MB
- 2025-08-22 Zenmap 7.98 34.56 MB
- 2025-05-14 Zenmap 7.97 34.09 MB
再看 5 筆
- 2025-05-07 Zenmap 7.96 34.04 MB
- 2024-04-23 Zenmap 7.95 32.4 MB
- 2023-05-21 Zenmap 7.94
- 2022-09-02 Zenmap 7.93
- 2021-08-08 Zenmap 7.92
這一版改了什麼
What's new in this version:
[Windows] Updated the bundled Npcap from 0.78 to 0.91, with several bugfixes for WiFi connectivity problems and stability issues.
Integrated all of your service/version detection fingerprints submitted from September to March (855 of them). The signature count went up 2.9% to 11,418. We now detect 1193 protocols from apachemq, bro, and clickhouse to jmon, slmp, and zookeeper.
[NSE] Added 14 NSE scripts from 12 authors, bringing the total up to 566! summaries are below:
Broadcast-ospf2-discover discovers OSPF 2 routers and neighbors. OSPFv2 authentication is supported.
Cics-info checks IBM TN3270 services for CICS transaction services and extracts useful information.
Cics-user-brute does brute-force enumeration of CICS usernames on IBM TN3270 services.
Http-cookie-flags checks HTTP session cookies for HTTPOnly and Secure flags.
Http-security-headers checks for the HTTP response headers related to security given in OWASP Secure Headers Project, giving a brief description of the header and its configuration value.
Http-vuln-cve2017-5638 checks for the RCE bug in Apache Struts2.
Http-vuln-cve2017-5689 detects a privilege escalation vulnerability (INTEL-SA-00075) in Intel Active Management Technology (AMT) capable systems.
Http-vuln-cve2017-1001000 detects a privilege escalation vulnerability in Wordpress 4.7.0 and 4.7.1.
Impress-remote-discover attempts to pair with the LibreOffice Impress presentation remote service and extract version info. Pairing is PIN-protected, and the script can optionally brute-force the PIN. New service probe and match line also added.
Smb-double-pulsar-backdoor detects the Shadow Brokers-leaked Double Pulsar backdoor in Windows SMB servers.
Smb-vuln-cve-2017-7494 detects a remote code execution vulnerability affecting Samba versions 3.5.0 and greater with writable shares.
Smb-vuln-ms17-010 detects a critical remote code execution vulnerability affecting SMBv1 servers in Microsoft Windows systems (ms17-010). The script also reports patched systems.
Tls-ticketbleed checks for the Ticketbleed vulnerability (CVE-2016-9244) in F5 BIG-IP appliances.
Vmware-version queries VMWare SOAP API for version and product information. Submitted in 2011, this was mistakenly turned into a service probe that was unable to elicit any matches.
[Ncat] A series of changes and fixes based on feedback from the Red Hat community:
Ncat will now continue trying to connect to each resolved address for a hostname before declaring the connection refused, allowing it to fallback from IPv6 to IPv4 or to connect to names that use DNS failover.
The --no-shutdown option now also works in connect mode, not only in listen mode.
Made -i/--idle-timeout not cause Ncat in server mode to close while waiting for an initial connection. This was also causing -i to interfere with the HTTP proxy server mode.
Ncat in server mode properly handles TLS renegotiations and other situations where SSL_read returns a non-fatal error. This was causing SSL-over-TCP connections to be dropped.
Enable --ssl-ciphers to be used with Ncat in client mode, not only in server (listen) mode.
[NSE] NSE libraries smb and msrpc now use fully qualified paths. SMB scripts now work against all modern versions of Microsoft Windows.
[NSE] smb library's share_get_list now properly uses anonymous connections first before falling back authenticating as a known user.
New service probes and matches for Apache HBase and Hadoop MapReduce.
Extended Memcached service probe and added match for Apache ZooKeeper.
[NSE] New script argument "vulns.short" will reduce vulns library script output to a single line containing the target name or IP, the vulnerability state, and the CVE ID or title of the vulnerability.
[NSE] SNMP scripts will now take a community string provided like `--script-args creds.snmp=private`, which previously did not work because it was interpreted as a username.
[NSE] Resolved several issues in the default HTTP redirect rules:
- A redirect is now cancelled if the original URL contains embedded credentials.
- A redirect test is now more careful in determining whether a redirect destination is related to the original host
- A redirect is now more strict in avoiding possible redirect loops
- [NSE] The HTTP Host header will now include the port unless it is the default one for a given scheme
- [NSE] The HTTP response object has a new member, fragment, which contains a partially received body (if any) when the overall request fails to complete
- [NSE]NSE now allows cookies to have arbitrary attributes, which are silently ignored (in accordance with RFC 6265). Unrecognized attributes were previously causing HTTP requests with such cookies to fail
- [NSE] NSE now correctly parses a Set-Cookie header that has unquoted whitespace in the cookie value (which is allowed per RFC 6265)
- [NSE] NSE is now able to process HTTP responses with a Set-Cookie header that has an extraneous trailing semicolon
- [NSE] TLS SNI now works correctly for NSE HTTP requests initiated with option any_af. As an added benefit, option any_af is now available for all connections via comm.lua, not just HTTP requests
- [NSE] There is a new common function, url.get_default_port(), to obtain the default port number for a given scheme
- [NSE] Function url.parse() now returns the port part as a number, not a string
- No longer allow ICMP Time Exceeded messages to mark a host as down during host discovery. Running traceroute at the same time as Nmap was causing interference
- [NSE] Fixed a JSON library issue that was causing long integers to be expressed in the scientific/exponent notation
- [NSE] Fixed several potential hangs in NSE scripts that used receive_buf(pattern), which will not return if the service continues to send data that does not match pattern. A new function in match.lua, pattern_limit, is introduced to limit the number of bytes consumed while searching for the pattern
- [Nsock] Handle any and all socket connect errors the same: raise as an Nsock error instead of fatal. This prevents Nmap and Ncat from quitting with "Strange error from connect:"
- [NSE] Added several commands to redis-info to extract listening addresses, connected clients, active channels, and cluster nodes
- [NSE] Refreshed script http-robtex-reverse-ip, reflecting changes at the source site
- [NSE] Added 8 new http-enum fingerprints for Hadoop infrastructure components
- [NSE] Added two new fingerprints to http-default-accounts (APC Management Card, older NetScreen ScreenOS)
- [NSE] Fix for oracle-tns-version which was sending an invalid TNS probe due to a string escaping mixup
- [NSE] ike-version now outputs information about supported attributes and unknown vendor ids. Also, a new fingerprint for FortiGate VPNs was submitted by Alexis La Goutte
- Enabled support for TLS SNI on the Windows platform
- New service probe and match lines for the JMON and RSE services of IBM Explorer for z/OS
- Removed a duplicate service probe for Memcached added in 2011 (the original probe was added in 2008) and reported as duplicate in 2013
- New service probe and match line for NoMachine NX Server remote desktop
- [Zenmap] Fixed a recurring installation problem on OS X/macOS where Zenmap was installed to /Applications/Applications/Zenmap.app instead of /Applications/Zenmap.app
- [Zenmap] Zenmap will no longer crash when no suitable temporary directory is found
- [Zenmap] Zenmap now properly handles the -v0 (no output) option, which was added in Nmap 7.10. Previously, this was treated the same as not specifying -v at all
- Updated or removed some OpenSSL library calls that were deprecated in OpenSSL 1.1
- [NSE] Script ssh-hostkey now recognizes and reports Ed25519 keys
- [NSE] Fixed script hang in several brute scripts due to the "threads" script-arg not being converted to a number. Error message was "nselib/brute.lua:1188: attempt to compare number with string"