
這是歷史版本頁面 — 看 Zenmap 最新版本
不會用Nmap指令?Zenmap把網路掃描變圖形介面
 Zenmap 7.70
資料更新 2018-03-21
閱讀約 5 分鐘
你剛接手公司網管,或只是想搞清楚家裡網路到底連了哪些裝置。你知道要掃描網路、檢查哪些電腦開了哪些連接埠,但打開命令提示字元輸入指令時,參數一堆根本記不住,輸出結果密密麻麻看不懂。你需要的是一個能幫你把這些事變簡單的工具,而不是再去背指令手冊。
一般人的做法是上網找指令教學,複製貼上然後祈禱結果正確。但Nmap指令參數組合太多,不同掃描類型要配不同參數,貼錯一個字母結果就完全不一樣。這類工具的切入點是:把複雜的指令包裝成圖形介面,用表單和按鈕取代打字,讓你能專注在「想掃什麼」而不是「指令怎麼寫」。
01Zenmap是什麼,跟Nmap有什麼關係?
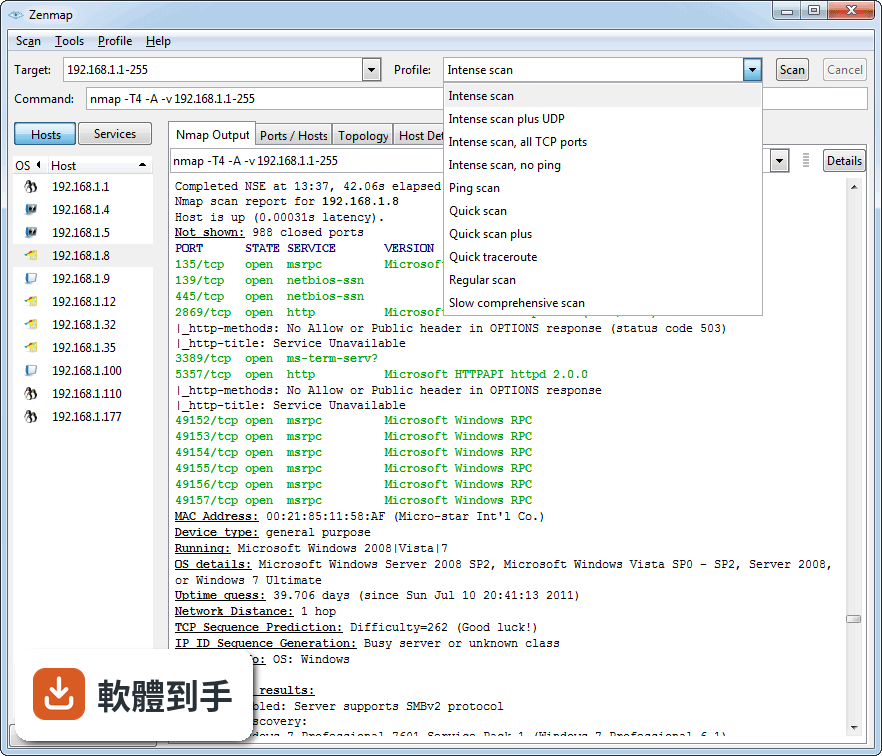
Zenmap是Nmap的官方圖形介面。Nmap本身是命令列工具,功能很強但必須用鍵盤輸入指令。Zenmap把這些指令包裝成視窗介面,你可以在欄位裡輸入目標IP或網域名稱,選好掃描類型,按一下按鈕就開始掃描。安裝Zenmap時會一起裝好Nmap,不需要分開處理。
02這套軟體能掃描哪些目標,只能掃一台電腦嗎?
可以掃描多個目標。除了單一IP位址,也支援輸入IP範圍或子網路,例如192.168.1.0/24這種寫法。也可以直接輸入主機名稱。掃描結果會列出所有找到的裝置、開啟的連接埠和服務,方便你一次掌握整個網路的狀況。
03掃描結果除了看連接埠,還能看到什麼資訊?
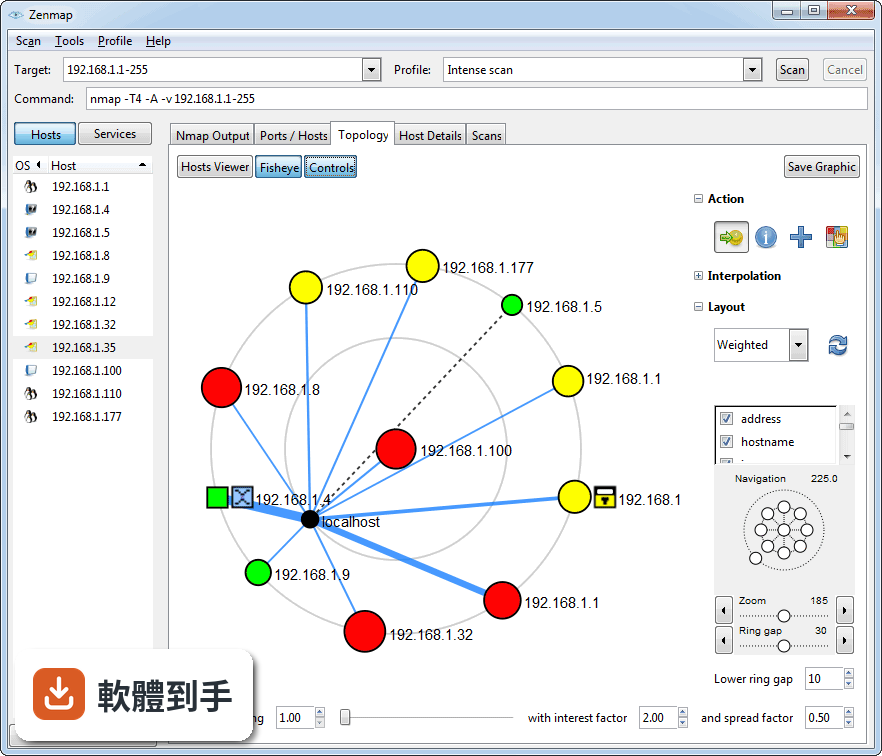
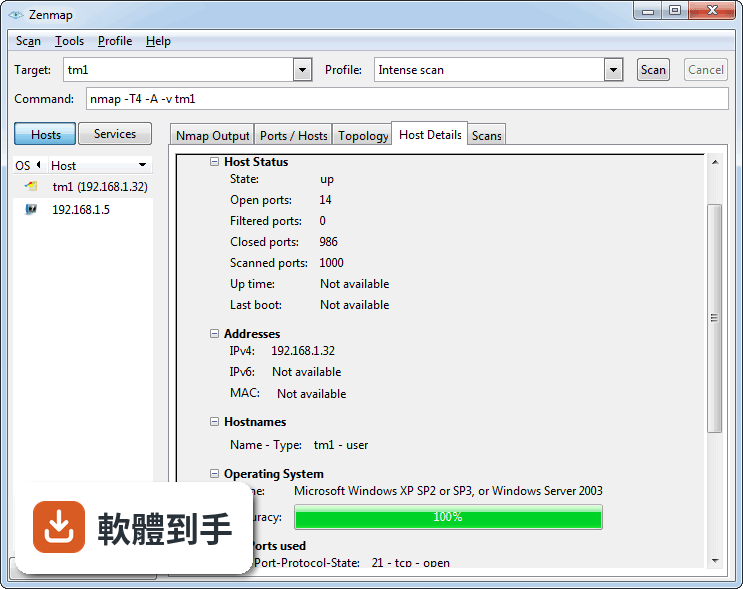
結果分幾個分頁顯示。除了連接埠和服務,還能看到主機詳細資料,包含作業系統偵測結果。另外有拓撲圖分頁,用圖形方式畫出網路裝置之間的連線關係。掃描紀錄會自動保存,之後可以回頭比對不同時間的掃描結果,看網路有沒有出現新的裝置或開啟新的連接埠。
04掃描結果可以存下來嗎?
可以。結果能匯出成XML或純文字格式,方便之後分析或記錄。如果你需要把掃描結果交給別人看,或自己留底比對,這個功能很實用。匯出後可以用其他工具開啟,或直接文字編輯器檢視。
05執行掃描需要管理員權限嗎?
要看掃描類型。基本的掃描可能不需要,但某些掃描像是作業系統偵測或SYN掃描,官方建議要有管理員權限才能完整執行。安裝時也需要管理員權限。如果你在一般使用者帳號下執行,可能會遇到部分功能無法使用的情況。
06我完全不懂網路指令,用這套軟體會卡關嗎?
它的設計就是讓不熟悉命令列的人也能用Nmap。介面有預設的掃描設定檔,例如「Intense scan」和「Quick scan」,直接選就能開始掃描。輸入目標位址、選好設定、按掃描,流程很直覺。不過掃描結果的解讀還是需要一些網路基礎知識,例如知道連接埠號碼代表的服務。
07這套軟體適合哪些人使用?
適合需要做網路安全稽核或管理的IT人員、滲透測試人員和系統管理員。如果你工作上需要定期檢查網路裝置、管理服務升級時程、監控主機或服務是否正常運作,這套軟體能幫你把Nmap的功能用圖形介面操作。對於想學習Nmap的人來說,也可以先從圖形介面理解掃描概念,再慢慢接觸指令。
08這套軟體還在持續更新嗎?
開發更新不算頻繁,屬於偶爾更新的狀態,但官方說明指出它仍然可以搭配新版本的Nmap正常運作。如果你擔心相容性問題,安裝時會一起安裝Nmap,兩者版本會搭配好。介面外觀比較舊,不是現代化的設計風格,但功能上沒有太大問題。
09介面只有英文,看不懂怎麼辦?
這套軟體的介面語系只有英文,沒有繁體中文。如果你英文閱讀有困難,操作上會比較吃力。不過主要欄位和按鈕的英文不算太複雜,配合線上教學或翻譯工具可以克服。如果完全無法接受英文介面,可以考慮其他有中文介面的掃描工具,但功能上可能沒有這麼完整。
10有沒有更簡單的替代軟體?
有。Angry IP Scanner、Advanced IP Scanner、SoftPerfect Network Scanner都是功能相近的掃描工具,介面更簡單,適合只想快速掃描IP和連接埠的使用者。但這些工具的進階功能不如Zenmap完整,例如拓撲圖、掃描紀錄比對、複雜的Nmap參數設定。如果你的需求只是偶爾掃一下網路,這些輕量工具可能更適合。
11非技術人員用這套軟體會遇到什麼困難?
官方說明提到,這套軟體對非技術使用者來說可能難以負擔。雖然圖形介面降低了指令門檻,但掃描結果的判讀、參數的選擇、權限的處理都需要網路基礎知識。如果你只是想知道家裡有哪些裝置連上Wi-Fi,用路由器管理介面或手機App可能更直接。這套軟體是給需要深入分析網路的人用的。
12這套軟體需要付費嗎?
不需要。它是開放原始碼軟體,可以免費下載使用。安裝程式會同時安裝Nmap和Zenmap,不需要額外購買授權。如果你之後想改用其他工具,也因為它是開放原始碼,社群有相關資源可以參考。
下載與官方連結
nmap-7.70-setup.exe · 26.25 MB · 連結指向軟體原廠
版本紀錄
- 2026-03-27 Zenmap 7.99 35.25 MB
- 2025-08-22 Zenmap 7.98 34.56 MB
- 2025-05-14 Zenmap 7.97 34.09 MB
再看 5 筆
- 2025-05-07 Zenmap 7.96 34.04 MB
- 2024-04-23 Zenmap 7.95 32.4 MB
- 2023-05-21 Zenmap 7.94
- 2022-09-02 Zenmap 7.93
- 2021-08-08 Zenmap 7.92
這一版改了什麼
What's new in this version:
- [Windows] Updated the bundled Npcap from 0.93 to 0.99-r2, with many stability fixes and installation improvements, as well as fixes to raw 802.11 frame capture
- Integrated all of your service/version detection fingerprints submitted from March 2017 to August 2017 (728 of them). The signature count went up 1.02% to 11,672, including 26 new softmatches. We now detect 1224 protocols from filenet-pch, lscp, and netassistant to sharp-remote, urbackup, and watchguard. We will try to integrate the remaining submissions in the next release.
- Integrated all of your IPv4 OS fingerprint submissions from September 2016 to August 2017 (667 of them). Added 298 fingerprints, bringing the new total to 5,652. Additions include iOS 11, macOS Sierra, Linux 4.14, Android 7, and more.
- Integrated all 33 of your IPv6 OS fingerprint submissions from September 2016 to August 2017. New groups for OpenBSD 6.0 and FreeBSD 11.0 were added, as well as strengthened groups for Linux and OS X.
- Added the --resolve-all option to resolve and scan all IP addresses of a host. This essentially replaces the resolveall NSE script. [Daniel Miller]
- [NSE][SECURITY] Nmap developer nnposter found a security flaw (directory traversal vulnerability) in the way the non-default http-fetch script sanitized URLs. If a user manualy ran this NSE script with against a malicious web server, the server could potentially (depending on NSE arguments used) cause files to be saved outside the intended destination directory. Existing files couldn't be overwritten. We fixed http-fetch, audited our other scripts to ensure they didn't make this mistake, and we updated the httpspider library API to protect against this by default. [nnposter, Daniel Miller]
[NSE] Added 9 NSE scripts, from 8 authors, bringing the total up to 588, the summaries are below:
- deluge-rpc-brute performs brute-force credential testing against Deluge BitTorrent RPC services, using the new zlib library. [Claudiu Perta]
- hostmap-crtsh lists subdomains by querying Google's Certificate Transparency logs. [Paulino Calderon]
- [GH#892] http-bigip-cookie decodes unencrypted F5 BIG-IP cookies and reports back the IP address and port of the actual server behind the load-balancer. [Seth Jackson]
- http-jsonp-detection Attempts to discover JSONP endpoints in web servers. JSONP endpoints can be used to bypass Same-origin Policy restrictions in web browsers. [Vinamra Bhatia]
- http-trane-info obtains information from Trane Tracer SC controllers and connected HVAC devices. [Pedro Joaquin]
- [GH#609] nbd-info uses the new nbd.lua library to query Network Block Devices for protocol and file export information. [Mak Kolybabi]
- rsa-vuln-roca checks for RSA keys generated by Infineon TPMs vulnerable to Return Of Coppersmith Attack (ROCA) (CVE-2017-15361). Checks SSH and TLS services. [Daniel Miller]
- [GH#987] smb-enum-services retrieves the list of services running on a remote Windows machine. Modern Windows systems requires a privileged domain account in order to list the services. [Rewanth Cool]
- tls-alpn checks TLS servers for Application Layer Protocol Negotiation (ALPN) support and reports supported protocols. ALPN largely replaces NPN, which tls-nextprotoneg was written for. [Daniel Miller]
- [GH#978] Fixed Nsock on Windows giving errors when selecting on STDIN. This was causing Ncat 7.60 in connect mode to quit with error: libnsock select_loop(): nsock_loop error 10038: An operation was attempted on something that is not a socket. [nnposter]
- [Ncat][GH#197][GH#1049] Fix --ssl connections from dropping on renegotiation, the same issue that was partially fixed for server mode in [GH#773]. Reported on Windows with -e by pkreuzt and vinod272. [Daniel Miller]
- [NSE][GH#1062][GH#1149] Some changes to brute.lua to better handle misbehaving or rate-limiting services. Most significantly, brute.killstagnated now defaults to true. Thanks to xp3s and Adamtimtim for reporing infinite loops and proposing changes.
- [NSE] VNC scripts now support Apple Remote Desktop authentication (auth type 30) [Daniel Miller]
- [NSE][GH#1111] Fix a script crash in ftp.lua when PASV connection timed out. [Aniket Pandey]
- [NSE][GH#1114] Update bitcoin-getaddr to receive more than one response message, since the first message usually only has one address in it. [h43z]
- [Ncat][GH#1139] Ncat now selects the correct default port for a given proxy type. [Pavel Zhukov]
- [NSE] memcached-info can now gather information from the UDP memcached service in addition to the TCP service. The UDP service is frequently used as a DDoS reflector and amplifier. [Daniel Miller]
- [NSE][GH#1129] Changed url.absolute() behavior with respect to dot and dot-dot path segments to comply with RFC 3986, section 5.2. [nnposter]
- Removed deprecated and undocumented aliases for several long options that used underscores instead of hyphens, such as --max_retries. [Daniel Miller]
- Improved service scan's treatment of soft matches in two ways. First of all, any probes that could result in a full match with the soft matched service will now be sent, regardless of rarity. This improves the chances of matching unusual services on non-standard ports. Second, probes are now skipped if they don't contain any signatures for the soft matched service. Previously the probes would still be run as long as the target port number matched the probe's specification. Together, these changes should make service/version detection faster and more accurate. For more details on how it works, see https://nmap.org/book/vscan.html. [Daniel Miller]
- --version-all now turns off the soft match optimization, ensuring that all probes really are sent, even if there aren't any existing match lines for the softmatched service. This is slower, but gives the most comprehensive results and produces better fingerprints for submission. [Daniel Miller]
- [NSE][GH#1083] New set of Telnet softmatches for version detection based on Telnet DO/DON'T options offered, covering a wide variety of devices and operating systems. [D Roberson]
- [GH#1112] Resolved crash opportunities caused by unexpected libpcap version string format. [Gisle Vanem, nnposter]
- [NSE][GH#1090] Fix false positives in rexec-brute by checking responses for indications of login failure. [Daniel Miller]
- [NSE][GH#1099] Fix http-fetch to keep downloaded files in separate destination directories. [Aniket Pandey]
[NSE] Added new fingerprints to http-default-accounts:
- Hikvision DS-XXX Network Camera and NUOO DVR [Paulino Calderon]
- [GH#1074] ActiveMQ, Purestorage, and Axis Network Cameras [Rob Fitzpatrick, Paulino Calderon]
- Added a new service detection match for WatchGuard Authentication Gateway. [Paulino Calderon]
- [NSE][GH#1038][GH#1037] Script qscan was not observing interpacket delays (parameter qscan.delay). [nnposter]
- [NSE][GH#1046] Script http-headers now fails properly if the target does not return a valid HTTP response. [spacewander]
- [Ncat][Nsock][GH#972] Remove RC4 from the list of TLS ciphers used by default, in accordance with RFC 7465. [Codarren Velvindron]
- [NSE][GH#1022] Fix a false positive condition in ipmi-cipher-zero caused by not checking the error code in responses. Implementations which return an error are not vulnerable. [Juho Jokelainen]
- [NSE][GH#958] Two new libraries for NSE.
- idna - Support for internationalized domain names in applications (IDNA)
- punycode (a transfer encoding syntax used in IDNA)
- [Rewanth Cool]
[NSE] New fingerprints for http-enum:
- [GH#954] Telerik UI CVE-2017-9248 [Harrison Neal]
- [GH#767] Many WordPress version detections [Rewanth Cool]
[GH#981][GH#984][GH#996][GH#975] Fixed Ncat proxy authentication issues:
- Usernames and/or passwords could not be empty
- Passwords could not contain colons
- SOCKS5 authentication was not properly documented
- SOCKS5 authentication had a memory leak
- [nnposter]
- [GH#1009][GH#1013] Fixes to autoconf header files to allow autoreconf to be run. [Lukas Schwaighofer]
- [GH#977] Improved DNS service version detection coverage and consistency by using data from a Project Sonar Internet wide survey. Numerouse false positives were removed and reliable softmatches added. Match lines for version.bind responses were also conslidated using the technique below. [Tom Sellers]
- [GH#977] Changed version probe fallbacks so as to work cross protocol (TCP/UDP). This enables consolidating match lines for services where the responses on TCP and UDP are similar. [Tom Sellers]
- [NSE][GH#532] Added the zlib library for NSE so scripts can easily handle compression. This work started during GSOC 2014, so we're particularly pleased to finally integrate it! [Claudiu Perta, Daniel Miller]
- [NSE][GH#1004] Fixed handling of brute.retries variable. It was being treated as the number of tries, not retries, and a value of 0 would result in infinite retries. Instead, it is now the number of retries, defaulting to 2 (3 total tries), with no option for infinite retries.
- [NSE] http-devframework-fingerprints.lua supports Jenkins server detection and returns extra information when Jenkins is detected [Vinamra Bhatia]
- [GH#926] The rarity level of MS SQL's service detection probe was decreased. Now we can find MS SQL in odd ports without increasing version intensity. [Paulino Calderon]
- [GH#957] Fix reporting of zlib and libssh2 versions in "nmap --version". We were always reporting the version number of the included source, even when a different version was actually linked. [Pavel Zhukov]
- Add a new helper function for nmap-service-probes match lines: $I(1,">") will unpack an unsigned big-endian integer value up to 8 bytes wide from capture 1. The second option can be "<" for little-endian. [Daniel Miller]