
這是歷史版本頁面 — 看 Zenmap 最新版本
不會用Nmap指令?Zenmap把網路掃描變圖形介面
 Zenmap 7.90
資料更新 2020-10-03
閱讀約 5 分鐘
你剛接手公司網管,或只是想搞清楚家裡網路到底連了哪些裝置。你知道要掃描網路、檢查哪些電腦開了哪些連接埠,但打開命令提示字元輸入指令時,參數一堆根本記不住,輸出結果密密麻麻看不懂。你需要的是一個能幫你把這些事變簡單的工具,而不是再去背指令手冊。
一般人的做法是上網找指令教學,複製貼上然後祈禱結果正確。但Nmap指令參數組合太多,不同掃描類型要配不同參數,貼錯一個字母結果就完全不一樣。這類工具的切入點是:把複雜的指令包裝成圖形介面,用表單和按鈕取代打字,讓你能專注在「想掃什麼」而不是「指令怎麼寫」。
01Zenmap是什麼,跟Nmap有什麼關係?
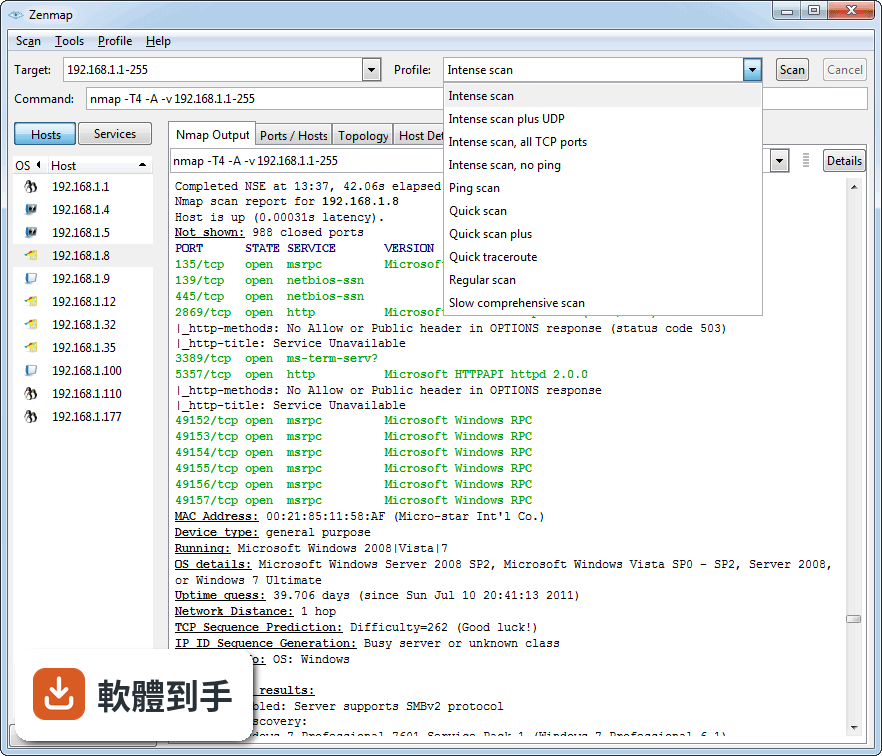
Zenmap是Nmap的官方圖形介面。Nmap本身是命令列工具,功能很強但必須用鍵盤輸入指令。Zenmap把這些指令包裝成視窗介面,你可以在欄位裡輸入目標IP或網域名稱,選好掃描類型,按一下按鈕就開始掃描。安裝Zenmap時會一起裝好Nmap,不需要分開處理。
02這套軟體能掃描哪些目標,只能掃一台電腦嗎?
可以掃描多個目標。除了單一IP位址,也支援輸入IP範圍或子網路,例如192.168.1.0/24這種寫法。也可以直接輸入主機名稱。掃描結果會列出所有找到的裝置、開啟的連接埠和服務,方便你一次掌握整個網路的狀況。
03掃描結果除了看連接埠,還能看到什麼資訊?
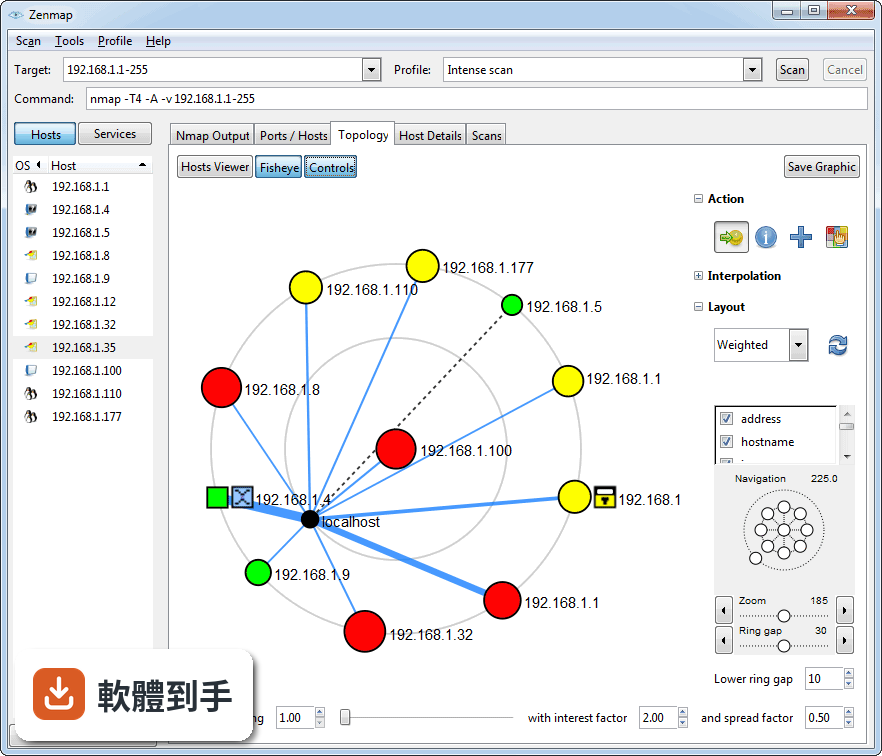
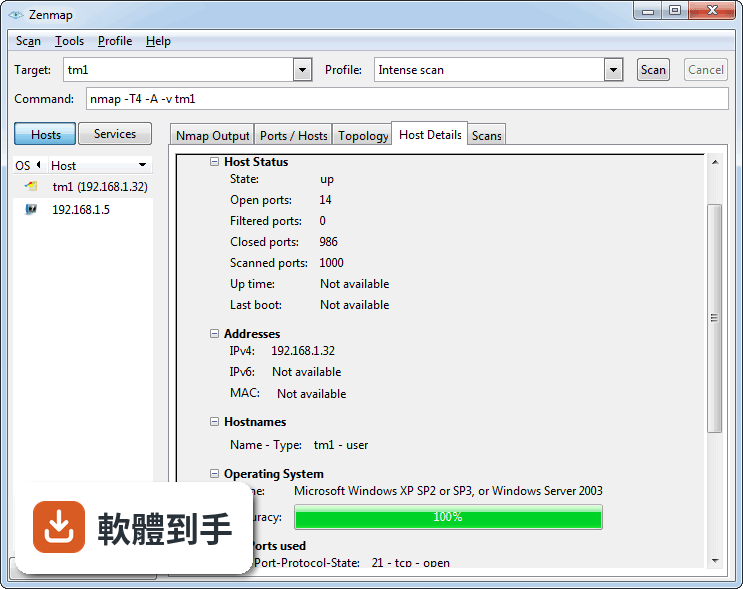
結果分幾個分頁顯示。除了連接埠和服務,還能看到主機詳細資料,包含作業系統偵測結果。另外有拓撲圖分頁,用圖形方式畫出網路裝置之間的連線關係。掃描紀錄會自動保存,之後可以回頭比對不同時間的掃描結果,看網路有沒有出現新的裝置或開啟新的連接埠。
04掃描結果可以存下來嗎?
可以。結果能匯出成XML或純文字格式,方便之後分析或記錄。如果你需要把掃描結果交給別人看,或自己留底比對,這個功能很實用。匯出後可以用其他工具開啟,或直接文字編輯器檢視。
05執行掃描需要管理員權限嗎?
要看掃描類型。基本的掃描可能不需要,但某些掃描像是作業系統偵測或SYN掃描,官方建議要有管理員權限才能完整執行。安裝時也需要管理員權限。如果你在一般使用者帳號下執行,可能會遇到部分功能無法使用的情況。
06我完全不懂網路指令,用這套軟體會卡關嗎?
它的設計就是讓不熟悉命令列的人也能用Nmap。介面有預設的掃描設定檔,例如「Intense scan」和「Quick scan」,直接選就能開始掃描。輸入目標位址、選好設定、按掃描,流程很直覺。不過掃描結果的解讀還是需要一些網路基礎知識,例如知道連接埠號碼代表的服務。
07這套軟體適合哪些人使用?
適合需要做網路安全稽核或管理的IT人員、滲透測試人員和系統管理員。如果你工作上需要定期檢查網路裝置、管理服務升級時程、監控主機或服務是否正常運作,這套軟體能幫你把Nmap的功能用圖形介面操作。對於想學習Nmap的人來說,也可以先從圖形介面理解掃描概念,再慢慢接觸指令。
08這套軟體還在持續更新嗎?
開發更新不算頻繁,屬於偶爾更新的狀態,但官方說明指出它仍然可以搭配新版本的Nmap正常運作。如果你擔心相容性問題,安裝時會一起安裝Nmap,兩者版本會搭配好。介面外觀比較舊,不是現代化的設計風格,但功能上沒有太大問題。
09介面只有英文,看不懂怎麼辦?
這套軟體的介面語系只有英文,沒有繁體中文。如果你英文閱讀有困難,操作上會比較吃力。不過主要欄位和按鈕的英文不算太複雜,配合線上教學或翻譯工具可以克服。如果完全無法接受英文介面,可以考慮其他有中文介面的掃描工具,但功能上可能沒有這麼完整。
10有沒有更簡單的替代軟體?
有。Angry IP Scanner、Advanced IP Scanner、SoftPerfect Network Scanner都是功能相近的掃描工具,介面更簡單,適合只想快速掃描IP和連接埠的使用者。但這些工具的進階功能不如Zenmap完整,例如拓撲圖、掃描紀錄比對、複雜的Nmap參數設定。如果你的需求只是偶爾掃一下網路,這些輕量工具可能更適合。
11非技術人員用這套軟體會遇到什麼困難?
官方說明提到,這套軟體對非技術使用者來說可能難以負擔。雖然圖形介面降低了指令門檻,但掃描結果的判讀、參數的選擇、權限的處理都需要網路基礎知識。如果你只是想知道家裡有哪些裝置連上Wi-Fi,用路由器管理介面或手機App可能更直接。這套軟體是給需要深入分析網路的人用的。
12這套軟體需要付費嗎?
不需要。它是開放原始碼軟體,可以免費下載使用。安裝程式會同時安裝Nmap和Zenmap,不需要額外購買授權。如果你之後想改用其他工具,也因為它是開放原始碼,社群有相關資源可以參考。
下載與官方連結
nmap-7.90-setup.exe · 25.96 MB · 連結指向軟體原廠
版本紀錄
- 2026-03-27 Zenmap 7.99 35.25 MB
- 2025-08-22 Zenmap 7.98 34.56 MB
- 2025-05-14 Zenmap 7.97 34.09 MB
再看 5 筆
- 2025-05-07 Zenmap 7.96 34.04 MB
- 2024-04-23 Zenmap 7.95 32.4 MB
- 2023-05-21 Zenmap 7.94
- 2022-09-02 Zenmap 7.93
- 2021-08-08 Zenmap 7.92
這一版改了什麼
What's new in this version:
- Fix the "iocp" Nsock engine for Windows to be able to correctly handle PCAP read events. This engine is now the default for Windows, which should greatly improve performance over the previous default, the "poll" engine
- Restrict Nmap's search path for scripts and data files. NMAPDATADIR, defined on Unix and Linux as ${prefix}/share/nmap, will not be searched on Windows, where it was previously defined as C:Nmap . Additionally, the --script option will not interpret names as directory names unless they are followed by a '/'
- Removed nmap-update. This program was intended to provide a way to update data files and NSE scripts, but the infrastructure was never fielded. It depended on Subversion version control and would have required maintaining separate versions of NSE scripts for compatibility.
- Reduced CPU usage of OS scan by 50% by avoiding string copy operations and removing undocumented fingerprint syntax unused in nmap-os-db ('&' and '+' in expressions)
- Fix a regression in ARP host discovery left over from the move from massping to ultra_scan in Nmap 4.22SOC8 (2007) that sometimes resulted in missing ARP responses from targets near the end of a scan. Accuracy and speed are both improved
- Addressed over 250 code quality issues identified by LGTM.com, improving our code quality score from "C" to "A+"
Fix an assertion failure when unsolicited ARP response is received:
nmap:
- Target.cc:503: void Target::stopTimeOutClock(const timeval*): Assertion `htn.toclock_running == true' failed.
- [GH#1859] Allow multiple UDP payloads to be specified for a port in nmap-payloads. If the first payload does not get a response, the remaining payloads are tried round-robin. [Paul Miseiko, Rapid7]
- [GH#1860] 23 new UDP payloads and dozens more default ports for existing payloads developed for Rapid7's InsightVM scan engine. These speed up and ensure detection of open UDP services. [Paul Miseiko, Rapid7]
- [GH#1616] New option --discovery-ignore-rst tells Nmap to ignore TCP RST responses when determining if a target is up. Useful when firewalls are spoofing RST packets.
- [Ncat][GH#2087][GH#1927][GH#1928][GH#1974] It is now possible to override the value of TLS SNI via --ssl-servername
- [GH#2104] Fixed parsing of TCP options which would hang (infinite loop) if an option had an explicit length of 0. Affects Nmap 7.80 only. [Daniel Miller, Imed Mnif]
- Script ssh2-enum-algos would fail if the server initiated the key exchange before completing the protocol version exchange [Scott Ellis, nnposter]
- Fetching of SSH2 keys might fail because of key exchange confusion
- Performance of script afp-ls has been dramatically improved
- Parsing of AFP FPGetFileDirParms and FPEnumerateExt2FPEnumerateExt2 responses was not working correctly
- Eliminated false positives in script http-shellshock caused by simple reflection of HTTP request data
- SNMP scripts are now enabled on non-standard ports where SNMP has been detected
- MQTT library was using incorrect position when parsing received responses
- IPMI library was using incorrect position when parsing received responses
- Scripts ipmi-brute and deluge-rpc-brute were not capturing successfully brute-forced credentials
- Allow resuming IPv6 scans with --resume. The address parsing was assuming IPv4 addresses, leading to "Unable to parse ip" error. In a related fix, MAC addresses will not be parsed as IP addresses when resuming from XML
- [GH#1622][GH#2068] Fix reverse-DNS handling of PTR records that are not lowercase. Nmap was failing to identify reverse-DNS names when the DNS server delivered them like ".IN-ADDR.ARPA".
- [NSE][GH#1999][GH#2005] IKE library was not properly populating the protocol number in aggressive mode requests.
- [GH#1963] Added service fingerprinting for MySQL 8.x, Microsoft SQL Server 2019, MariaDB, and Crate.io CrateDB. Updated PostreSQL coverage and added specific detection of recent versions running in Docker.
- [NSE] New script uptime-agent-info collects system information from an Idera Uptime Infrastructure Monitor agent
- [NSE] New outlib library will consolidate functions related to NSE output, both string formatting conventions and structured output
- New XML output "hosthint" tag emitted during host discovery when a target is found to be up. This gives earlier notification than waiting for the hostgroup to finish all scan phases.
- [GH#917] New UDP payloads for GPRS Tunneling Protocol (GTP) on ports 2123, 2152, and 3386.
- [NSE][GH#1825] SSH scripts now run on several ports likely to be SSH based on empirical data from Shodan.io, as well as the netconf-ssh service.
- [Zenmap][GH#1777] Stop creating a debugging output file 'tmp.txt' on the desktop in macOS.
- [Nping] Address build failure under libc++ due to "using namespace std;" in several headers, resulting in conflicting definitions of bind(). Reported by StormBytePP and Rosen Penev
- [Ncat][GH#1868] Fix a fatal error when connecting to a Linux VM socket with verbose output enabled.
- [Ncat][GH#2060] Proxy credentials can be alternatively passed onto Ncat by setting environment variable NCAT_PROXY_AUTH, which reduces the risk of the credentials getting captured in process logs.
- [NSE][GH#1723] Fixed a crash on Windows when processing a GZIP-encoded HTTP body
- Upgrade libpcap to 1.9.1, which addresses several CVE vulnerabilities.
- Upgrade libssh2 to 1.9.0, fixing compilation with OpenSSL 1.1.0 API.
- [GH#1717][GH#1718] Processing of IP address CIDR blocks was not working correctly on ppc64, ppc64le, and s390x architectures.
- [Windows] Add support for the new loopback behavior in Npcap 0.9983. This enables Nmap to scan localhost on Windows without needing the Npcap Loopback Adapter to be installed, which was a source of problems for some users
- [NSE] MS SQL library has improved version resolution, from service pack level to individual cumulative updates
- [NSE][GH#2077] With increased verbosity, script http-default-accounts now reports matched target fingerprints even if no default credentials were found
- [NSE][GH#2063] IPP request object conversion to string was not working correctly
- [NSE][GH#2063] IPP response parser was not correctly processing end-of-attributes-tag
- [NSE] Script cups-info was failing due to erroneous double-decoding of the IPP printer status
- [NSE][GH#2010] Oracle TNS parser was incorrectly unmarshalling DALC byte arrays
- [NSE] The password hashing function for Oracle 10g was not working correctly for non-alphanumeric characters
- [NSE] Virtual host probing list, vhosts-full.lst, was missing numerous entries present in vhosts-default.lst
- [NSE][GH#1931][GH#1932] Script http-grep was not correctly calculating Luhn checksum
- [NSE][GH#1838] Scripts dhcp-discover and broadcast-dhcp-discover now support new argument "mac" to force a specific client MAC address
- [NSE] Code improvements in RPC Dump, benefitting NFS-related scripts
- [NSE] RPC code was using incorrect port range, which was causing some calls, such as NFS mountd, to fail intermittently
- [NSE][GH#1876] XML output from script ssl-cert now includes RSA key modulus and exponent
- [NSE][GH#1837] Nmap no longer crashes when SMB scripts, such as smb-ls, call smb.find_files
- [NSE][GH#1802] The MongoDB library was causing errors when assembling protocol payloads.
- [NSE][GH#1781][GH#1796] The RTSP library was not correctly generating request strings.
- [NSE][GH#1706] VNC handshakes were failing with insert position out of bounds error.
- [NSE][GH#1720] Function marshall_dom_sid2 in library msrpctypes was not correctly populating ID Authority.
- [NSE][GH#1720] Unmarshalling functions in library msrpctypes were attempting arithmetic on a nil argument. [Ivan Ivanov, nnposter]
- [NSE][GH#1720] Functions lsa_lookupnames2 and lsa_lookupsids2 in library msrpc were incorrectly referencing function strjoin when called with debug level 2 or higher.
- [NSE][GH#1755][GH#2096] Added HTTP default account fingerprints for Tomcat Host Manager and Dell iDRAC9
- [NSE][GH#1476][GH#1707] A MS-SMB spec non-compliance in Samba was causing protocol negotiation to fail with data string too short error
- [NSE][GH#1480][GH#1713][GH#1714] A bug in SMB library was causing scripts to fail with bad format argument error
- [NSE] New script, dicom-brute.nse, attempts to brute force the called Application Entity Title of DICOM servers
- [NSE] New script, dicom-ping.nse, discovers DICOM servers and determines if any Application Entity Title is allowed to connect
- [NSE] New library, dicom.lua, implements the DICOM protocol used for storing and transfering medical images
- [NSE][GH#1665] The HTTP library no longer crashes when code requests digest authentication but the server does not provide the necessary authentication header
- [NSE] Fixed a bug in http-wordpress-users.nse that could cause extraneous output to be captured as part of a username
- Added a UDP payload for STUN (Session Traversal Utilities for NAT)
- [NSE] Fixed an off-by-one bug in the stun.lua library that prevented parsing a server response